Matching Policies for Account and Session Takeover Prevention
Account and Session Takeover Prevention (ASTP) helps large consumer web applications protect their users from account compromise and fraud. It enables security and fraud teams to detect when user accounts or active login sessions have been stolen and take action before attackers cause harm.
- Access to this feature requires an add-on. Please reach out to your CSM for more information.
- Details on connecting to this data can be found in our API documentation.
This solution is built for consumer-facing digital platforms that manage large volumes of user accounts including, e-commerce platforms, financial services and fintech companies, social media and online communities, streaming and entertainment services, gaming platforms, cloud and AI service providers
These organizations face constant risk from fraud, account abuse, and reputational damage when attackers gain unauthorized access to user accounts.
ASTP Policies and How They Work
Flare continuously collects and analyzes data from sources where stolen credentials and session data are traded. This intelligence is continuously evaluated to:
- Check whether user credentials or sessions have been compromised
- Identify high-risk or actively abused sessions
- Trigger security actions such as session revocation or additional verification
This data can be leveraged through the following ASTP Matching Policies:
The Cookie Monitoring policy defines how Flare monitors cookies associated with a domain Identifier. It is available to customers who have subscribed to the Account and Session Takeover Prevention (ASTP) solution.
How it works: When a Cookie Monitoring policy is assigned to a domain Identifier, Flare scans incoming stealer logs for cookies matching the monitored domain. Matched cookies are securely stored and made accessible only to the tenant they belong to. Each policy can be assigned to any number of domain Identifiers.
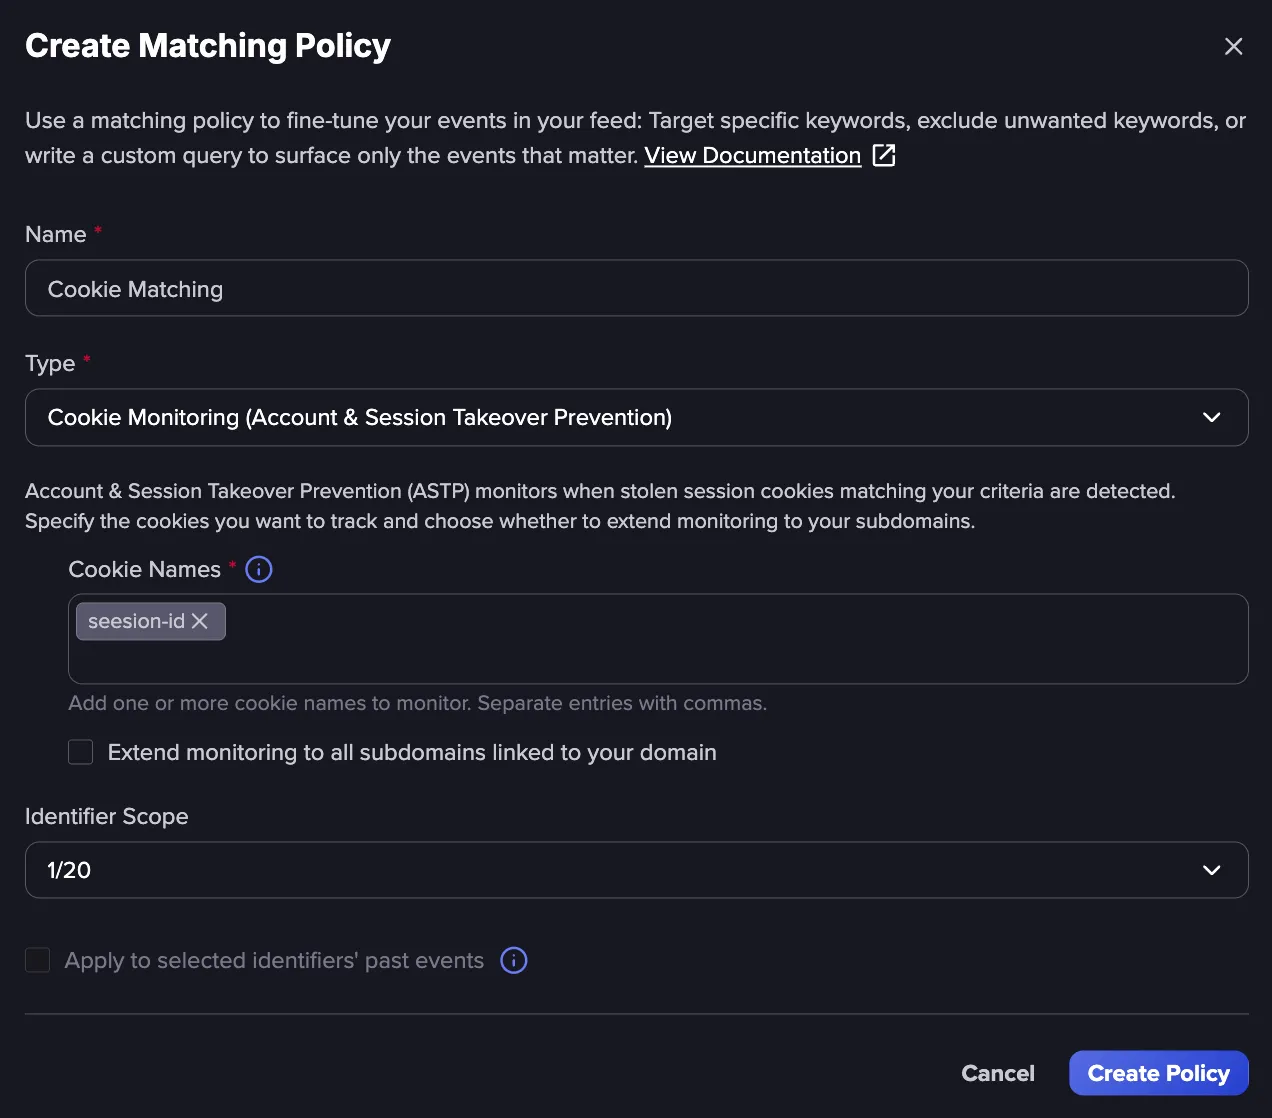
Configuration: Each Cookie Monitoring policy has the following configuration:
- Cookie Names: Enter the specific cookie names to monitor.
- Subdomain Monitoring: Select the Extend Monitoring to all subdomains linked to your domain, to include cookies from all subdomains.
- Identifier Scope: Select one or more Identifiers, or leave blank to apply to the whole Tenant.
For subdomain monitoring to work correctly, an active Identifier must exist for each subdomain. For example, if subdomain monitoring is enabled for flare.io, cookies from api.flare.io will only be ingested if an Identifier exists for api.flare.io. For more information on automatic subdomain discovery, see Discovery PoliciesDiscovery Policies.
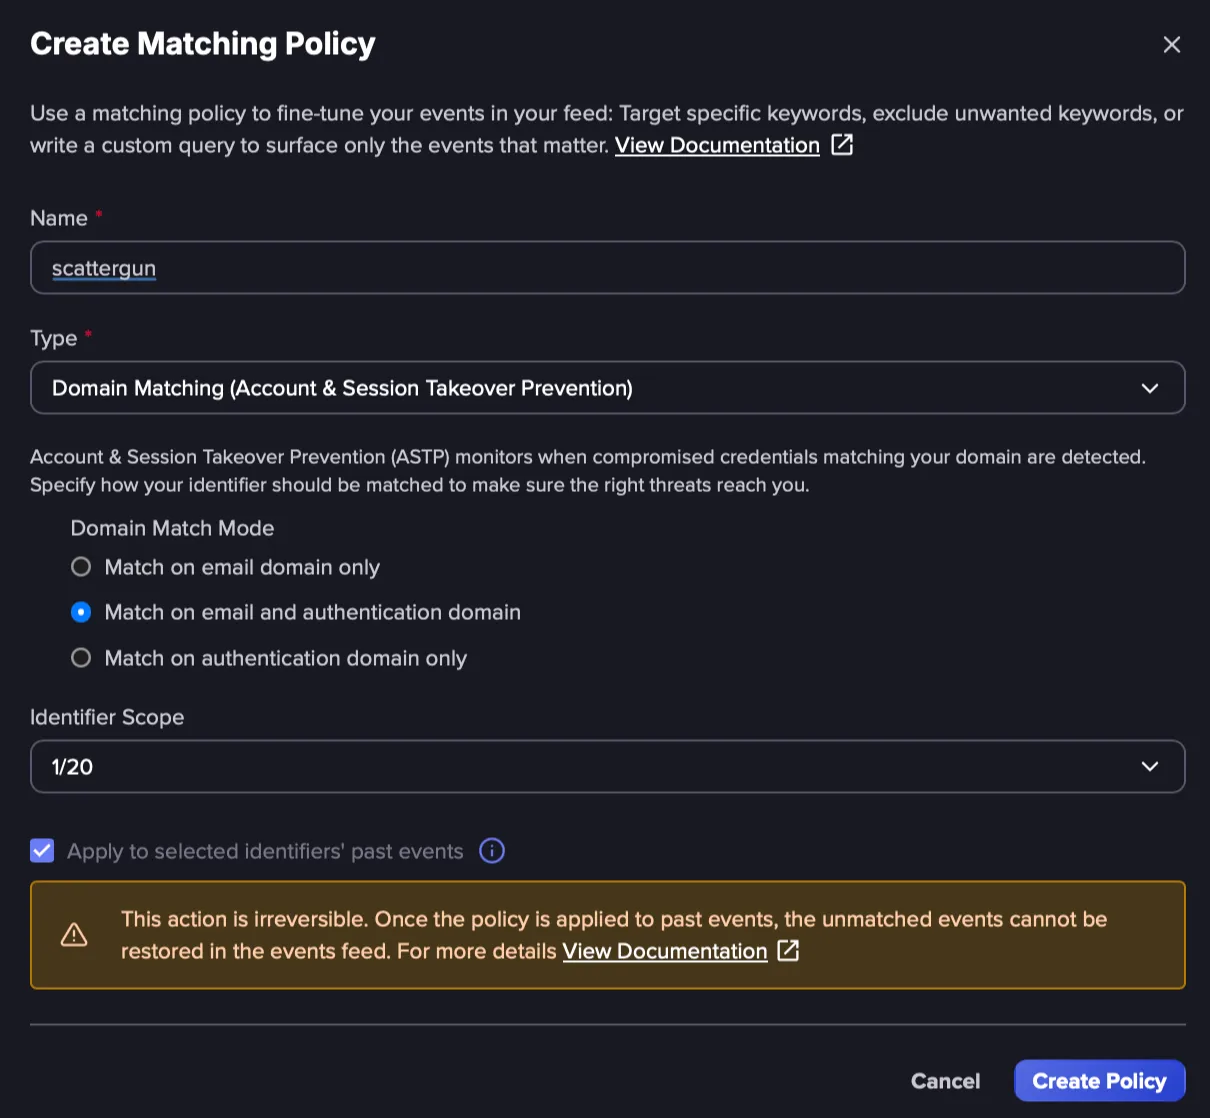
Creating an ASTP Policy
Follow the steps in this product tour to create an ASTP Matching Policy:
- Up to 10 Matching Policies can be assigned to an Identifier.
Key Features and Benefits
This solution is designed for organizations operating at internet scale, where millions of users and active sessions make traditional account takeover defenses difficult to manage. It provides organizations visibility into one of the most difficult-to-detect account takeover methods: stolen active sessions. By combining leaked credential intelligence with session-level risk detection, Flare helps teams proactively protect users, reduce fraud, and maintain trust at scale.
- Leaked Credentials Intelligence: Identify user accounts exposed through large-scale credential leaks.
- Stolen Session Detection: Detect active login sessions that attackers can use to bypass authentication.
- API-First Integration: Easily integrate Flare intelligence into fraud, security, or identity systems.
- Continuously Updated Threat Data: Intelligence is refreshed as new threats and stolen data emerge.
- Reduce Fraud and Abuse: Stop fraudulent transactions, bot activity, and account misuse earlier.
- Protect Customer Trust: Prevent unauthorized access that leads to customer frustration or churn.
- Lower Operational Burden: Avoid building and maintaining complex in-house monitoring for stolen sessions.
- Improve Security Without Excessive Friction: Target only high-risk sessions instead of applying blanket security measures to all users.
The Use Case: Preventing Account and Session Takeovers
Attackers increasingly bypass passwords and multi-factor authentication by stealing active login sessions from infected user devices. Once an attacker has a stolen session, they can access an account as if they were the legitimate user.
Flare helps organizations:
- Identify accounts exposed through leaked credentials
- Detect active sessions that have been stolen and are at risk
- Take action to revoke or reset compromised sessions
This allows teams to stop account takeovers earlier, before fraud, abuse, or customer impact occurs.