November 2026
Granular Events for Chat Messages and Ransomware Leaks
Release date: November 2, 2026
Chat message and ransomware leak events are now modeled as separate, individual events, enabling more precise analysis and more accurate search results.
- Chat messages: Each attachment is now its own independent event, separate from the chat message it was posted with. Attachments can be evaluated based on their own characteristics, and searches return matching attachments without false matches from the parent chat message. Learn moreLearn more
- Ransomware leaks: Each file listing is now its own independent event, separate from the ransomware leak blog post. File listings can be evaluated based on their own characteristics, and searches return matching file listings without false matches from the parent blog post. Learn moreLearn more
To effectively manage these events, the following two new Tenant Duplication Policies are now available.
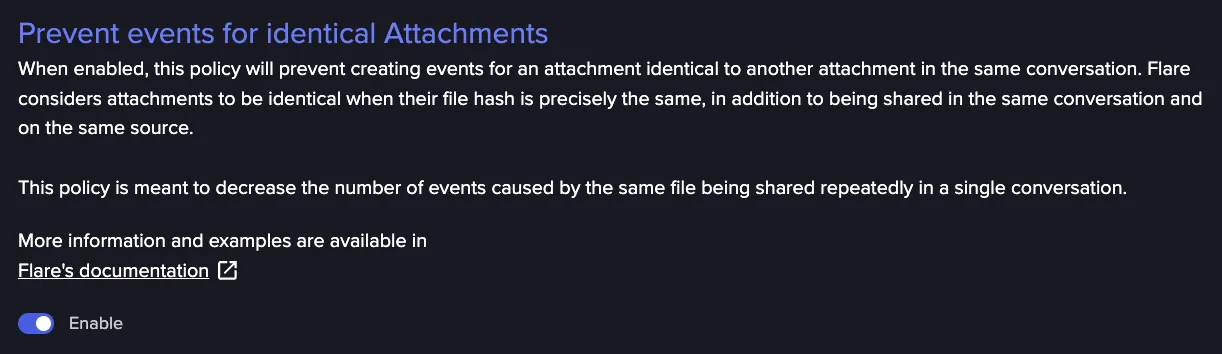
- Prevent Events for Identical Attachments
The new Prevent Events for Identical Attachments policy prevents event creation for an attachment identical to another attachment within the same conversation. The policy is enabled by default.
- When the policy is enabled, the first matching attachment in a conversation creates one event, and identical attachments shared later in the same conversation do not create additional events.
- When the policy is disabled, a new event is created for each matching attachment, including identical attachments shared multiple times in the same conversation.
Learn moreLearn more
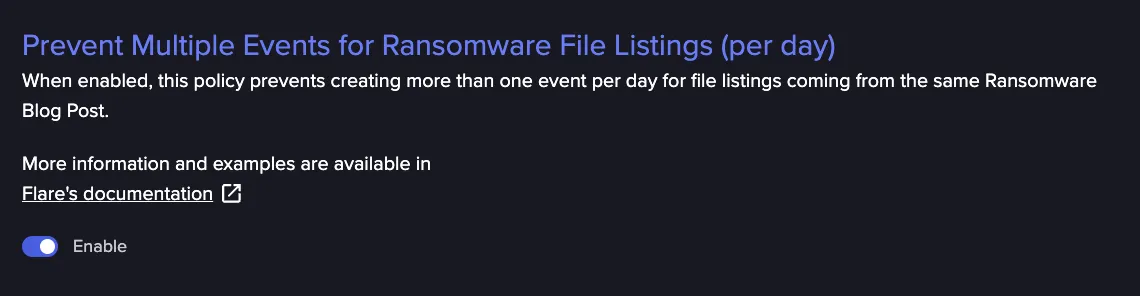
- Prevent Multiple Events for Ransomware File Listings
The new Prevent Multiple Events for Ransomware File Listings policy limits event creation to one file listing event per ransomware leak every 24 hours. This policy is enabled by default and is applied per ransomware leak, not per Identifier.
- When the policy is enabled, the first matching file listing for a ransomware leak creates one event, and no additional events are created for the same ransomware leak for the next 24 hours. All file listings from the ransomware leak remain available in the original event.
- When the policy is disabled, a new event is created for each matching file listing of a ransomware leak.
This reduces noise from large ransomware leaks that are collected over multiple days. However, if your triage process depends on being notified of every file listing for a ransomware leak, consider disabling this policy.
Learn moreLearn more
Labels on Infected Device (Stealer Logs) Events
Release date: November 2, 2026
Infected Device events are now automatically labeled with the actionable details found in each stealer log, so you can see what matters without digging through the raw data. Labels cover:
- Applications: Which apps have credentials in the log.
- Access Types: The kind of access exposed, such as access to an IdP.
- Facts: Device characteristics observed directly in the log.
- Findings: Conclusions drawn from several parts of the log, such as whether the listed location is likely accurate.
- PII: Whether personal information was exfiltrated.
Search and filter by label in the Flare platform to surface your highest-criticality stealer logs, cut noise, and spend less time on manual investigation. Labels are currently available in the platform only, with API support planned in a future release.
Learn moreLearn more
Labels on Forum Post and Chat Message Events
Release date: November 2, 2026
Forum and chat activity is now labeled so you can quickly tell what a mention of your organization actually means, whether it’s a data breach for sale, a fraud scheme, or a passing reference in an unrelated conversation.
- Forum Posts: Labeled with the thread topic and author intent.
- Chat Messages: Labeled with the topic only, since channels mix many authors and purposes.
Use labels to separate real threats from noise and prioritize what needs your attention.
Learn moreLearn more