The CTI Module
Flare's Cyber Threat Intelligence (CTI) Module brings threat intelligence research, reporting, operationalization, and investigation under one umbrella in the Flare Platform. With the CTI Module, you can:
- Research threat actors, campaigns, indicators of compromise (IOCs), tactics, techniques, and procedures (TTPs) in one place.
- Report findings in executive-ready format, scoped to your organization.
- Operationalize indicators by delivering high-volume IOC coverage with full STIX object relationships into existing security stacks.
- Analyze suspicious files and URLs is an isolated, evasion-resistant environment before you act on them. (available as an add-on)
When you encounter a threat, the CTI Module helps you understand who is behind it, whether the actor is credible, what campaign it belongs to, and what to do about it, all from the same platform and the same underlying intelligence.
Capabilities in the CTI Module
A complete CTI workflow offers four capabilities designed to hand off intelligence to one another, so an investigation can move from a single search to active defense without leaving the platform.
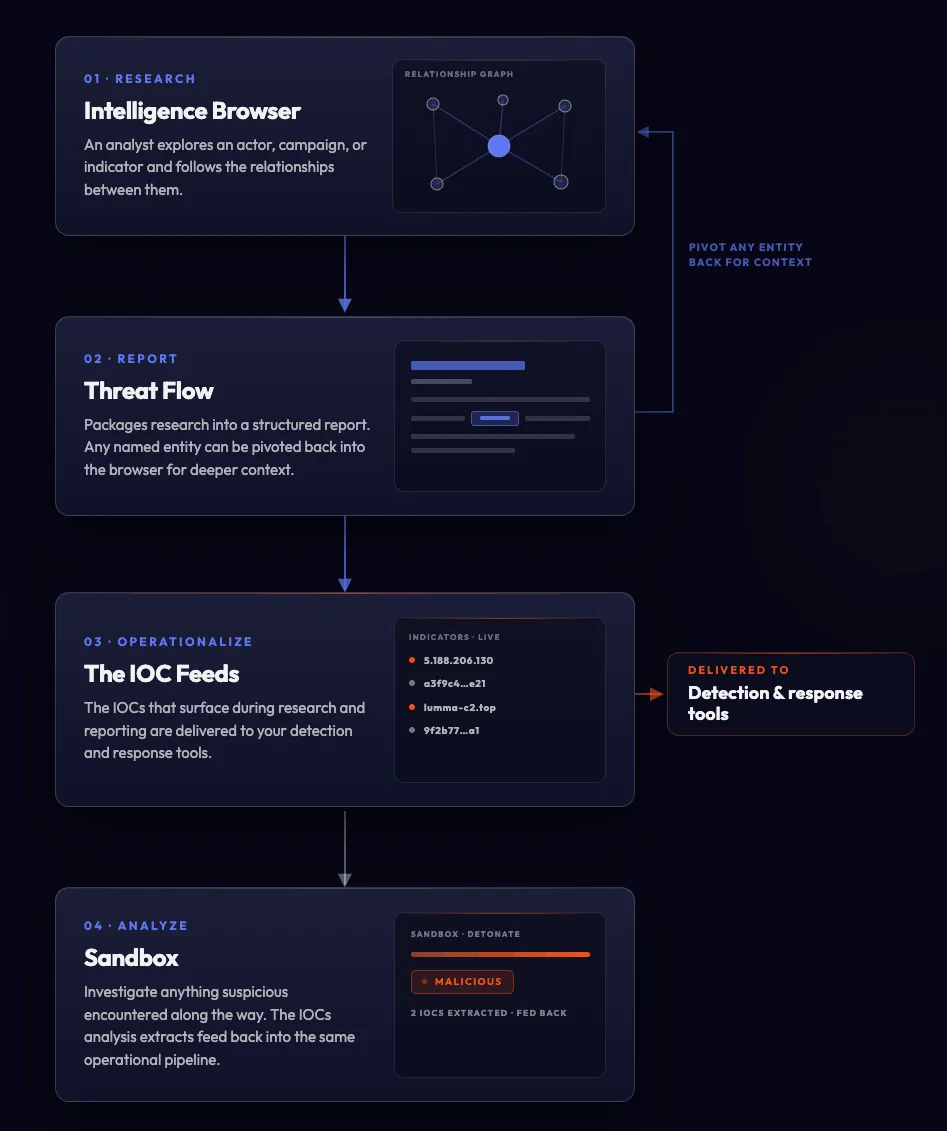
Together, these four capabilities cover the full investigation lifecycle: from signal, to context, to investigation, and to reporting.
- Access to this module requires an add-on. Please reach out to your CSM for more information.
Explore the CTI Module
Research threat actors, campaigns, indicators of compromise (IOCs), and tactics, techniques, and procedures (TTPs) across Flare's Collection and third-party libraries.
Threat Flowk
Generate technical and executive-ready intelligence reports with verdicts, extracted IOCs, recommendations, and mapped MITRE ATT&CK techniques.
IOC Feedse
Deliver high-volume IOC coverage with full STIX object relationships into your SIEM, SOAR, TIP, and EDR using the industry-standard STIX and TAXII protocols.
Sandboxs (add-on)
Investigate suspicious files and URLs in a private, evasion-resistant environment to see exactly how they behave before you act.