Lookalike Domains Event Category
Lookalike domains imitate your organization's real domains using tactics such as typosquatting, homoglyphs, and combosquatting. They are a primary vector for phishing and brand impersonation.
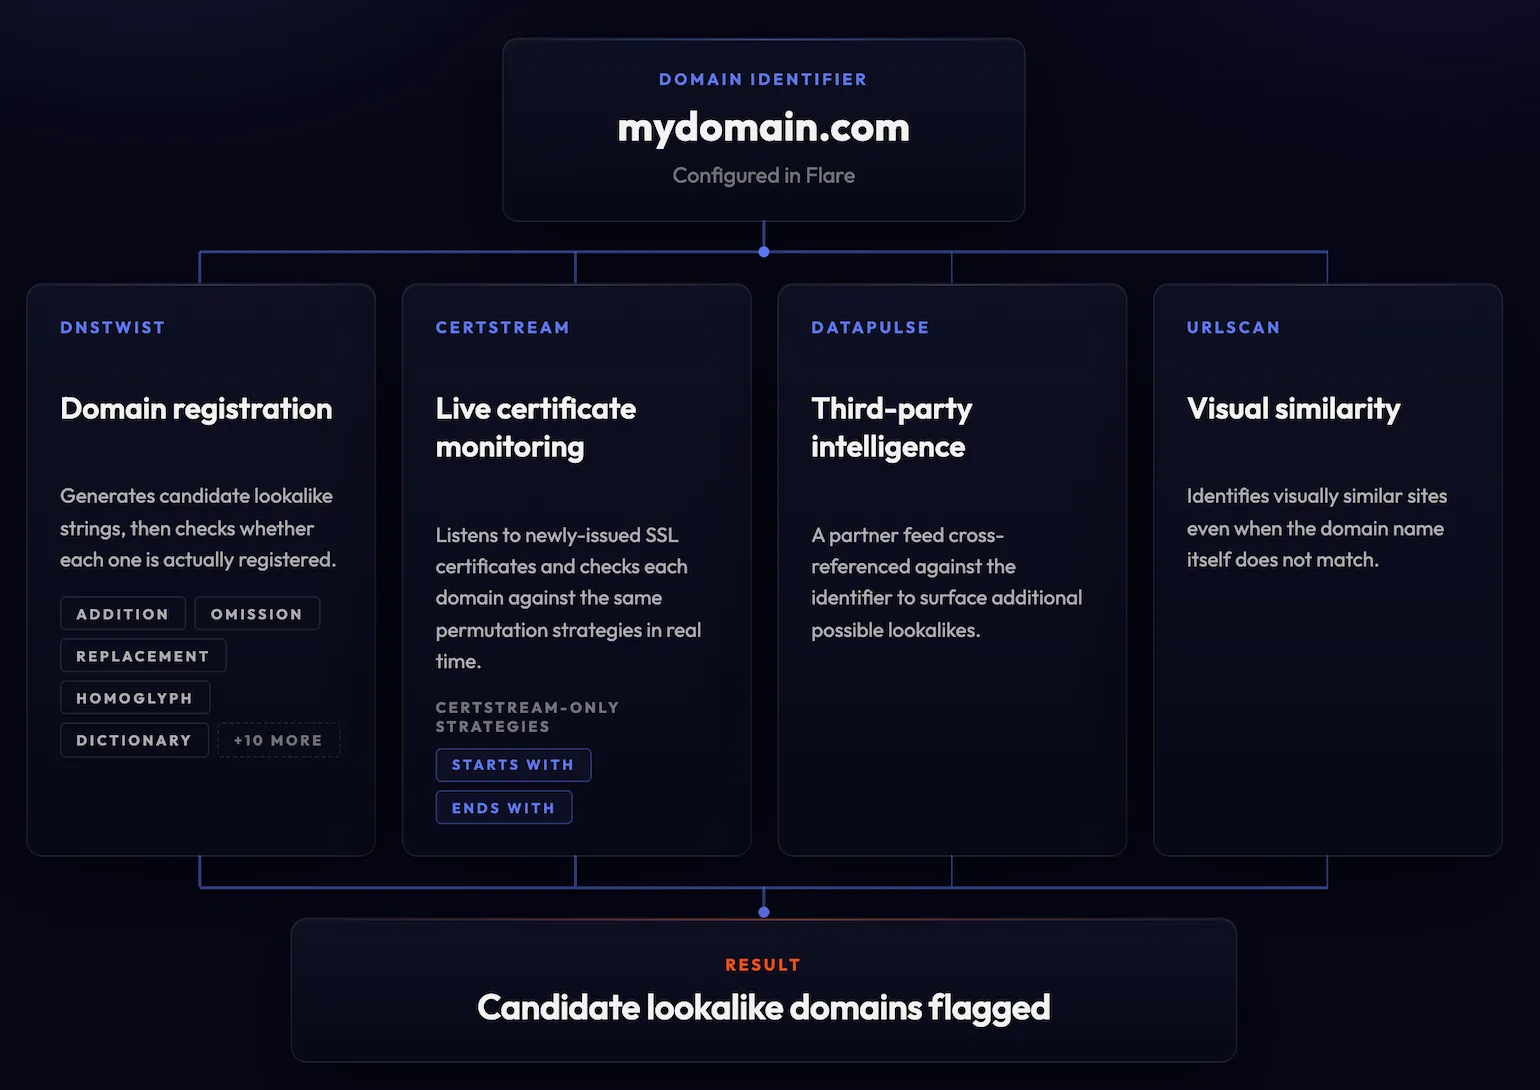
Flare monitors such domains continuously across several detection sources. Detection covers newly issued SSL certificates, domains that resolve in DNS, and domain intelligence from domain intelligence feeds. Because DNS-based detection evaluates all currently registered domains rather than only new ones, lookalike domains that were registered long before you added your Domain Identifier are surfaced. Visual similarity detection is also available in the extended tier.
The Lookalike Domains event category covers every event generated for a domain imitating one of your Domain Identifiers. These events appear in your Tenant Feed under the Lookalike Domains category.
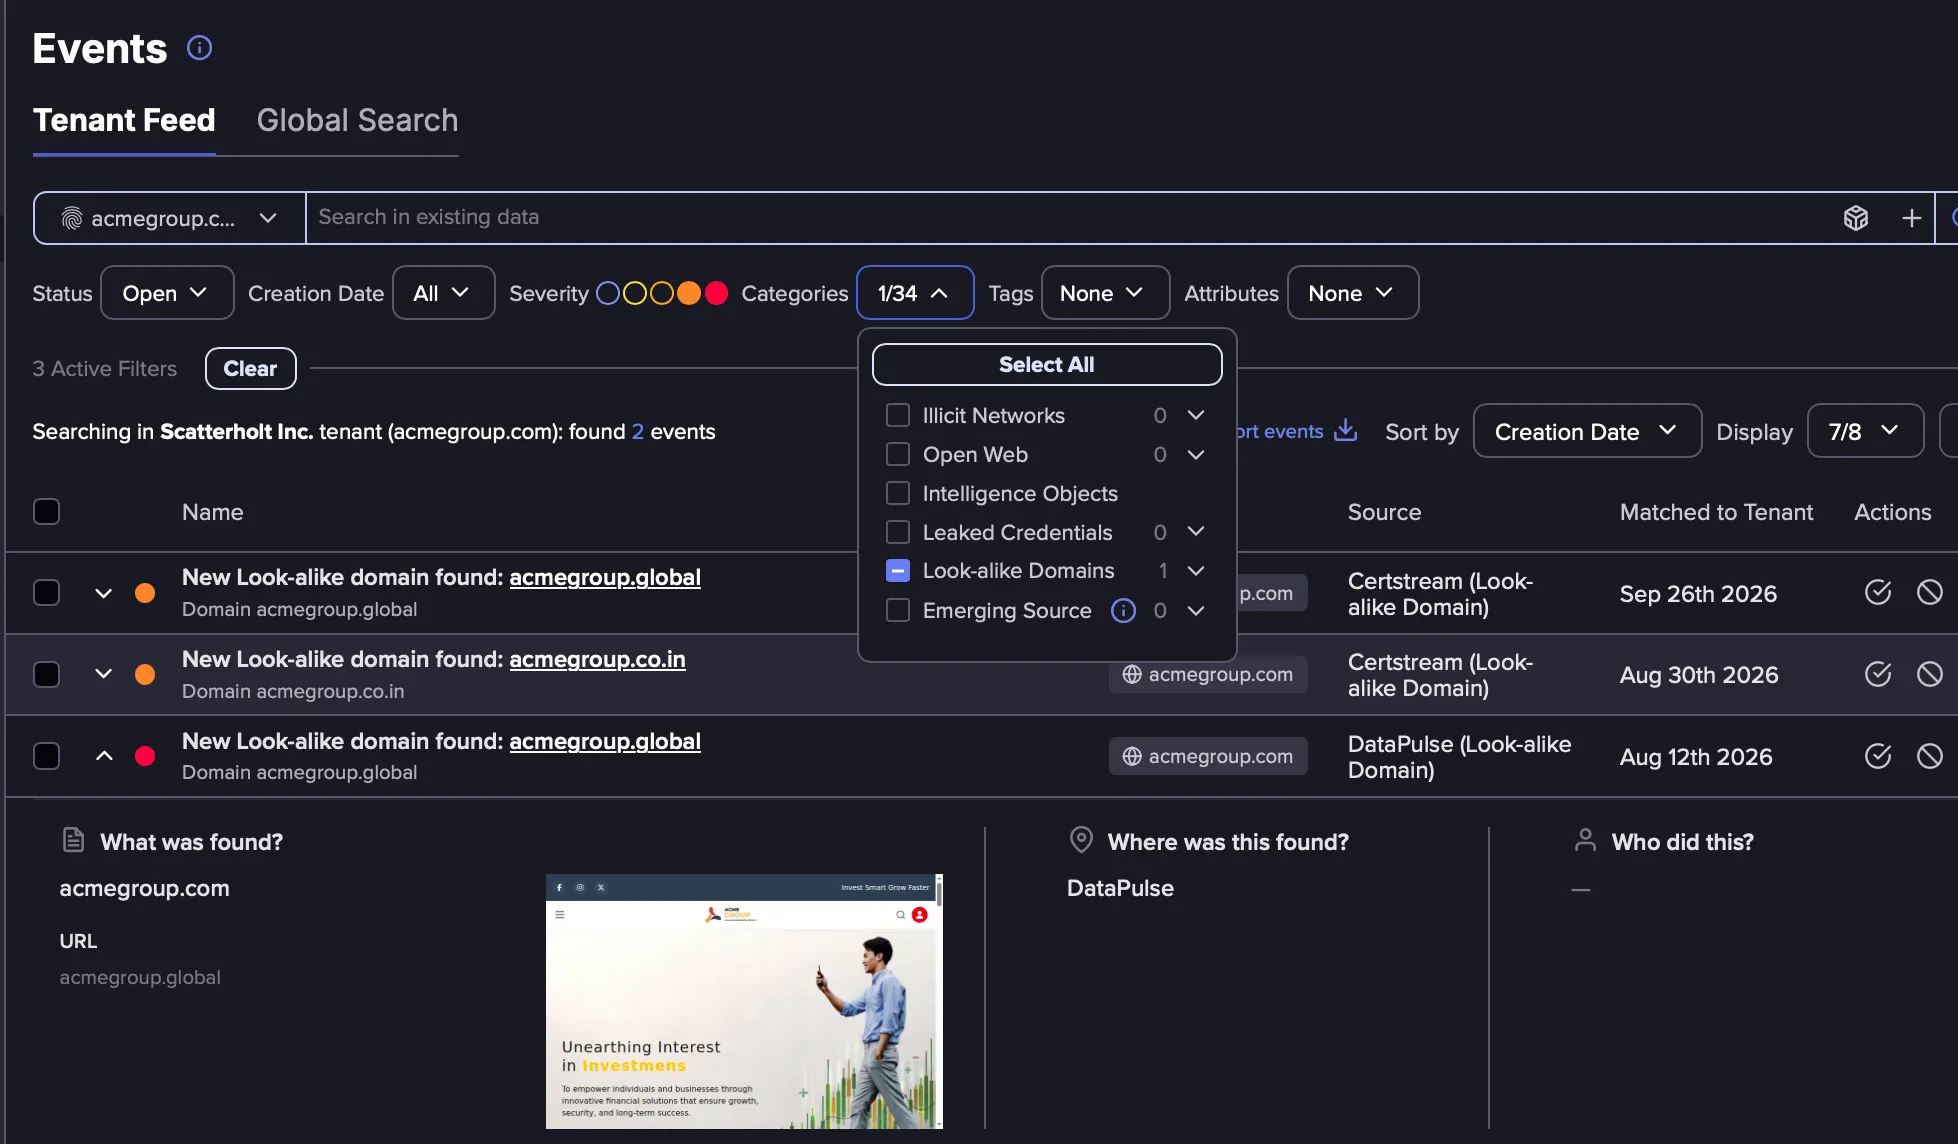
Lookalike Domains in the Tenant Feed
A lookalike domain typically moves through two stages. It is first registered, and often sits dormant on a parking page. It later becomes active, and its content and hosting infrastructure begin to change. Both stages are represented as separate events in the Tenant Feed.
Discovery Events
A Discovery Event is generated the first time a lookalike domain is identified for one of your Domain Identifiers. These events state that a new lookalike domain was found and include the details detected for it.
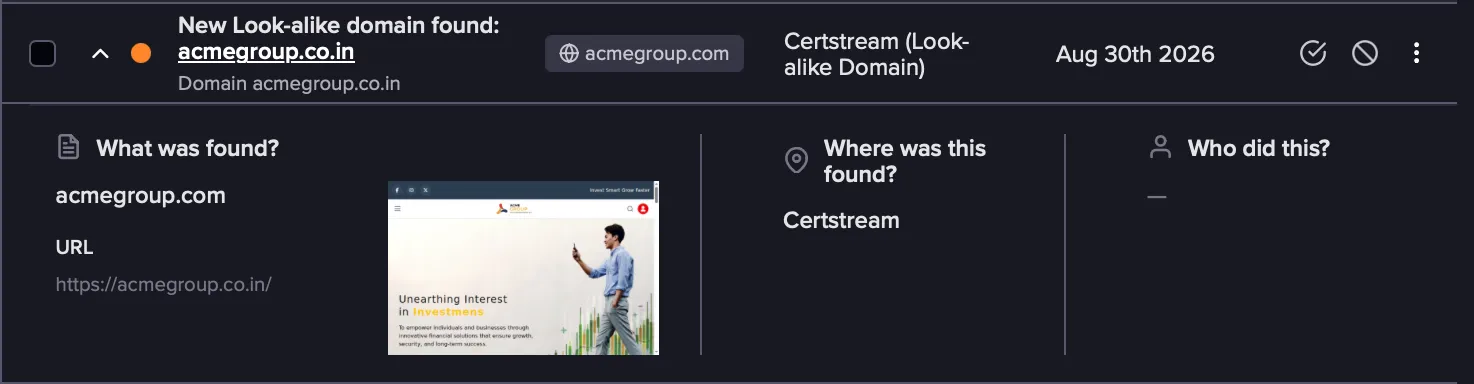
Discovery Events come from the following detection sources:
- Certificate Transparency Logs: Certificate transparency logs are monitored in real time and newly issued SSL certificates whose subject resembles one of your Domain Identifiers are flagged. Because this is a live stream, it does not return certificates issued before your Identifier was created.
- Domain Fuzzing: Generates permutations of your Domain Identifier and checks each one for active DNS records. It detects domains regardless of how long ago they were registered.
- Domain Intelligence Feeds: Domain Identifiers are also matched against intelligence from domain intelligence feeds to surface possible lookalikes, extending coverage beyond permutation-based and certificate-based detection.
- Visual Similarity Detection: Visual similarity detection surfaces sites resembling your own, even when the domain name itself is not similar.
Ignore a Lookalike Domain
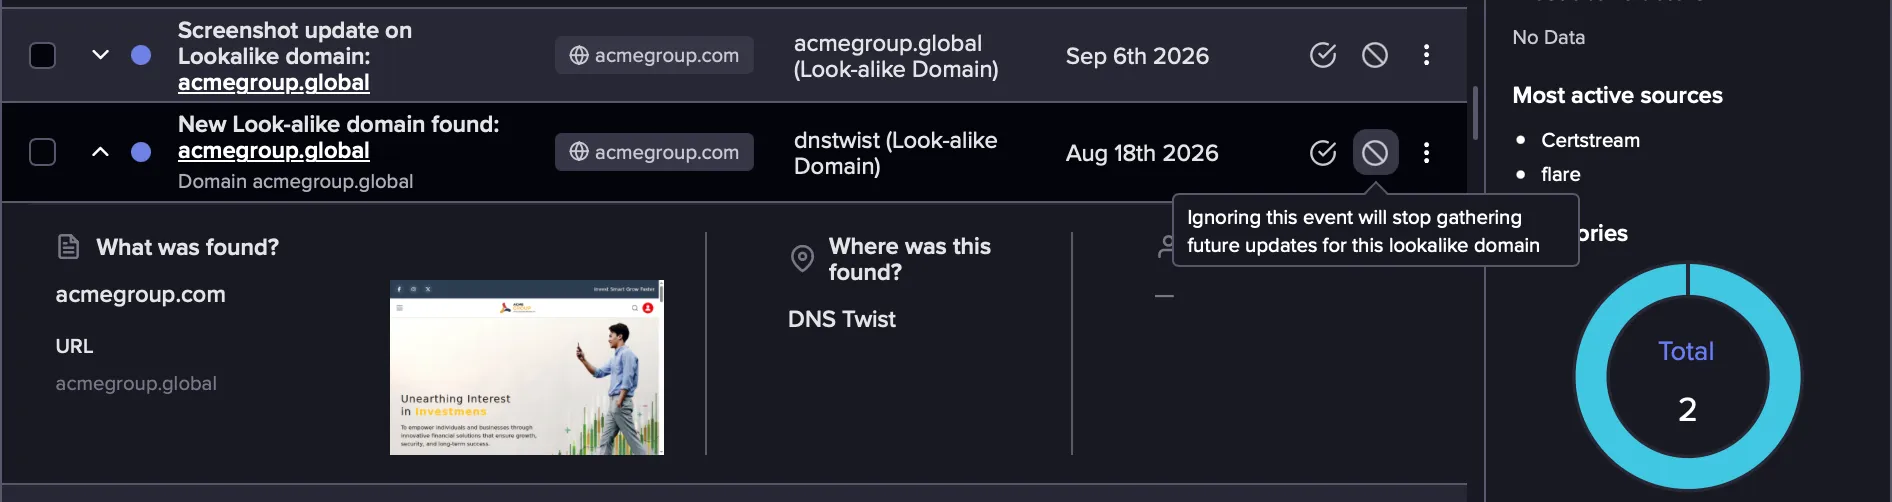
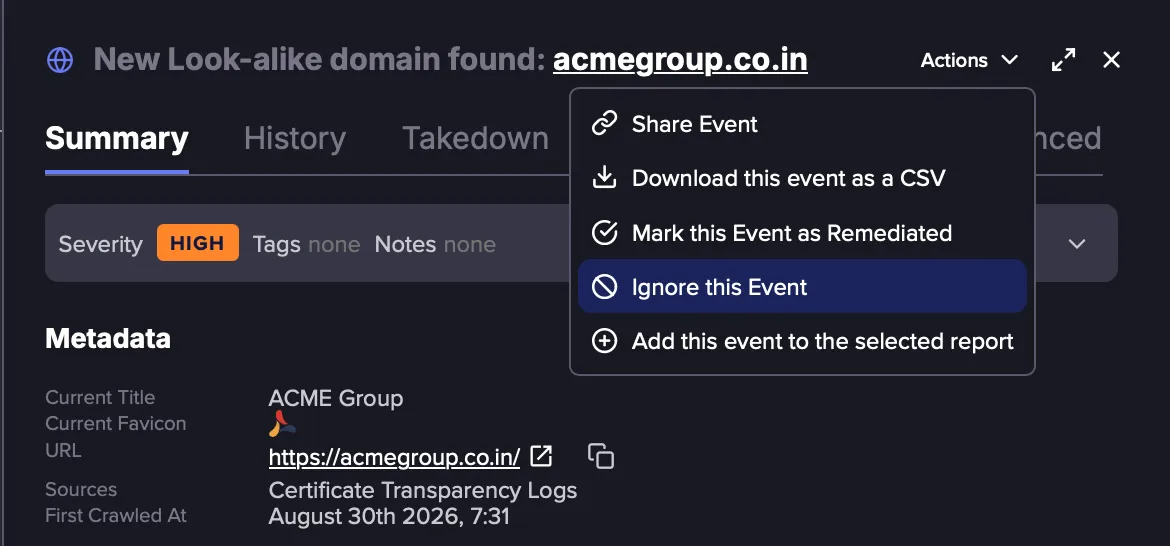
If a detected domain is legitimate or is not considered a threat, you can stop receiving future updates for it by ignoring its Discovery Event. This can be done either from the Tenant Feed or the details of the event.
- In the Tenant Feed, find the Discovery Event and click the Ignore this event icon.
- View details of an event and select Ignore this Event from the Actions menu.
Update Events
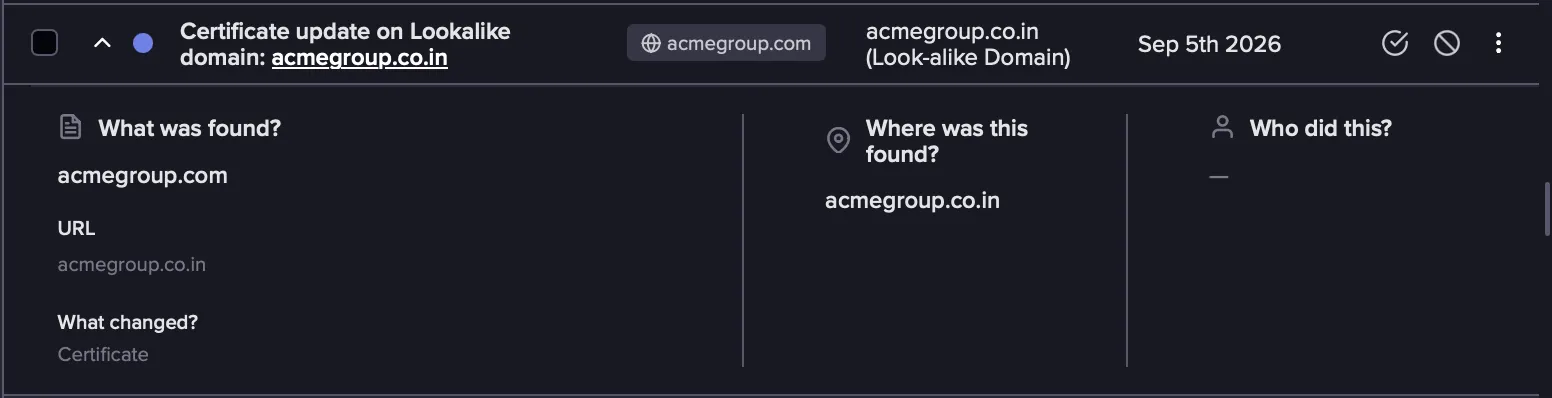
An Update Event is generated when a tracked attribute of a known lookalike domain changes. Each change generates a new event with its own severity assessment, so a domain that was low priority as a parked page is re-evaluated as soon as it begins to resemble your own. Because each change is a separate event, you can get AlertsAlerts on changes as they happen.
Update Events are currently being enabled progressively. If you do not see them yet and would like them enabled sooner, please contact your CSM.
What's Included in Update Events
Update Events are generated for the following attributes:
- Standard Lookalike Domain Monitoring: Base tracking covers following updates to a domain:
- Title Update: The domain's page title changes.
- Favicon Update: The domain's favicon changes.
- Screenshot Update: The domain's landing page screenshot changes.
- IP Address Update: The domain resolves to a new IP address.
- Extended Lookalike Domain Monitoring: With the extended tier, the following additional fields are also tracked:
- DNS Records Update: The domain's DNS records change, including MX records.
- WHOIS/RDAP Update: The domain's registration data changes, such as the registrar or registrant.
- SSL Certificate Update: A new SSL certificate is issued for the domain.
Extended Lookalike Domain Monitoring
Extended Lookalike Domain Monitoring includes access to the Lookalike Domains BrowserLookalike Domains Browser, where you can view all detected lookalike domains and their related events in one place.
Configuring Events for Lookalike Domains
To see Lookalike Domain Events in your Tenant Feed, enable them for your Domain Identifiers, then select them in the Tenant Feed filters and configure Alerts for them.
Step 1: Enable Lookalike Domain Events for an Identifier
Follow these steps when creating a Domain Identifier:
Navigate to the Identifiers page and click Create Identifier. For complete instructions on how to create an Identifier, see Configure IdentifiersConfigure Identifiers.
Select Domain as the type and enter a domain name.
From Threat Categories, select Domain Impersonation.
All Lookalike Domain sub-categories, including Discovery and Update Events, are selected by default. Clear any sub-categories you do not want to receive.
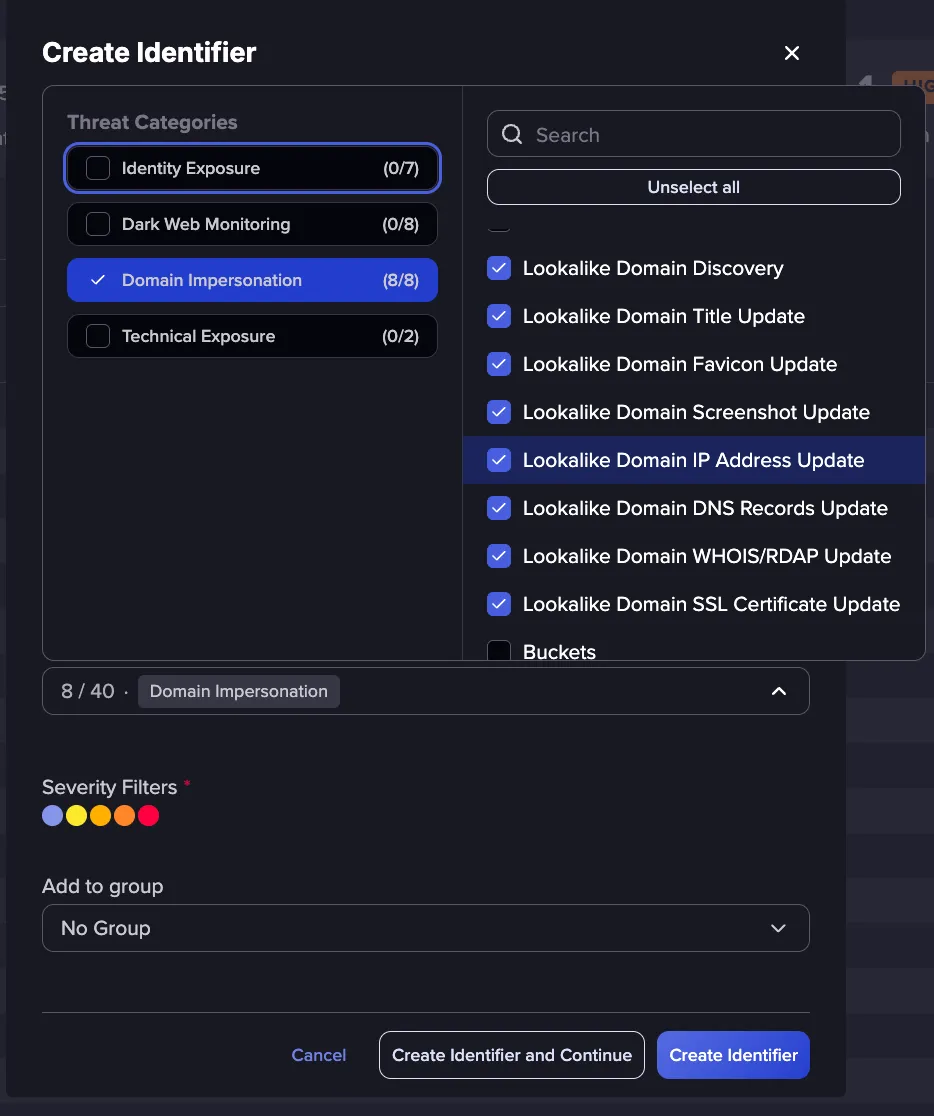
Complete the Identifier configuration and click Create Identifier.
Step 2: View Lookalike Domain Events in the Tenant Feed
Follow these steps to view events for lookalike domains in the Tenant Feed:
Navigate to the Events page and click the Categories filter in your Tenant Feed.
Expand the Lookalike Domains category and select the events you want to surface.
In the Tenant Feed, only the Domain Discovery event is enabled by default. Select one or more sub-categories to receive relevant Update Events.
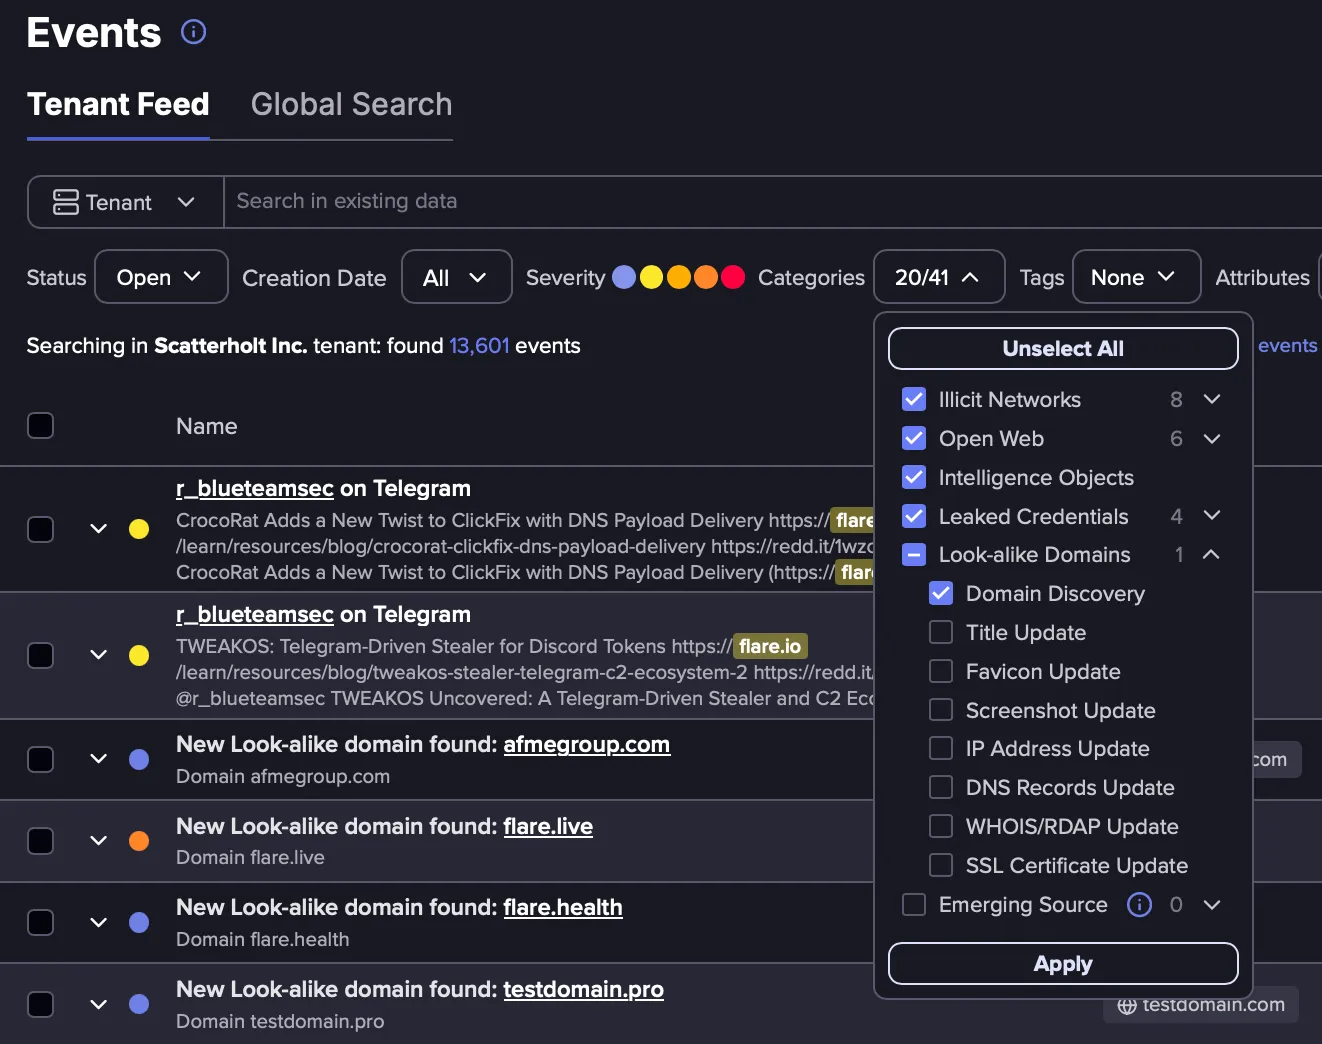
Click Apply.
Step 3: Configuring Alerts for Lookalike Domains
Follow these steps to configure Alerts for lookalike domains:
Navigate to the Alerts page and create a new Alert. For complete instructions on how to create an Alert, see Alert CentralAlert Central.
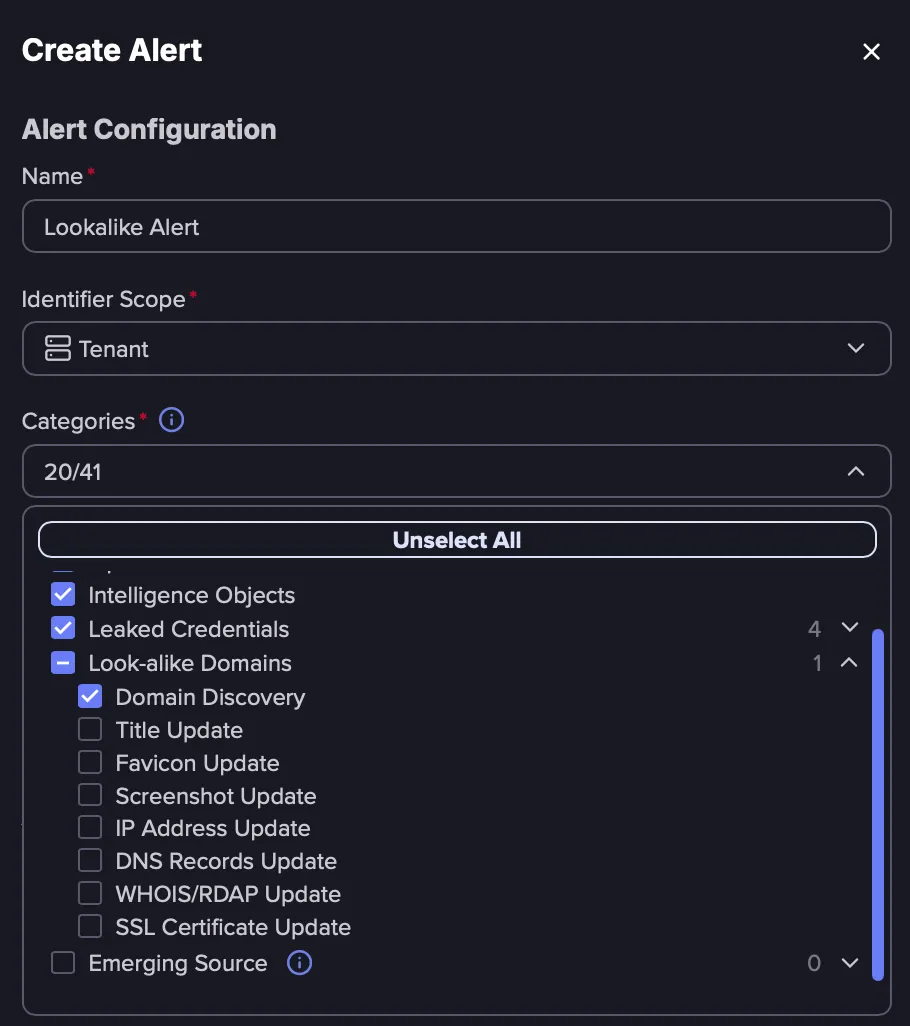
In the Categories setting, select one or more Lookalike Domains categories.
For Alerts, only the Domain Discovery event is enabled by default. Select one or more sub-categories to receive relevant Update Events.
How Detection Works
Lookalike domains are detected using the following methodology. Each pipeline runs on its own cadence, daily or weekly by strategy complexity. Certificate transparency logs are the exception, running continuously against the live certificate stream
For complete details on lookalike domain detection, including permutation strategies and scoring, see Lookalike Domains Data Sourced.